
Emerald Pages
◆
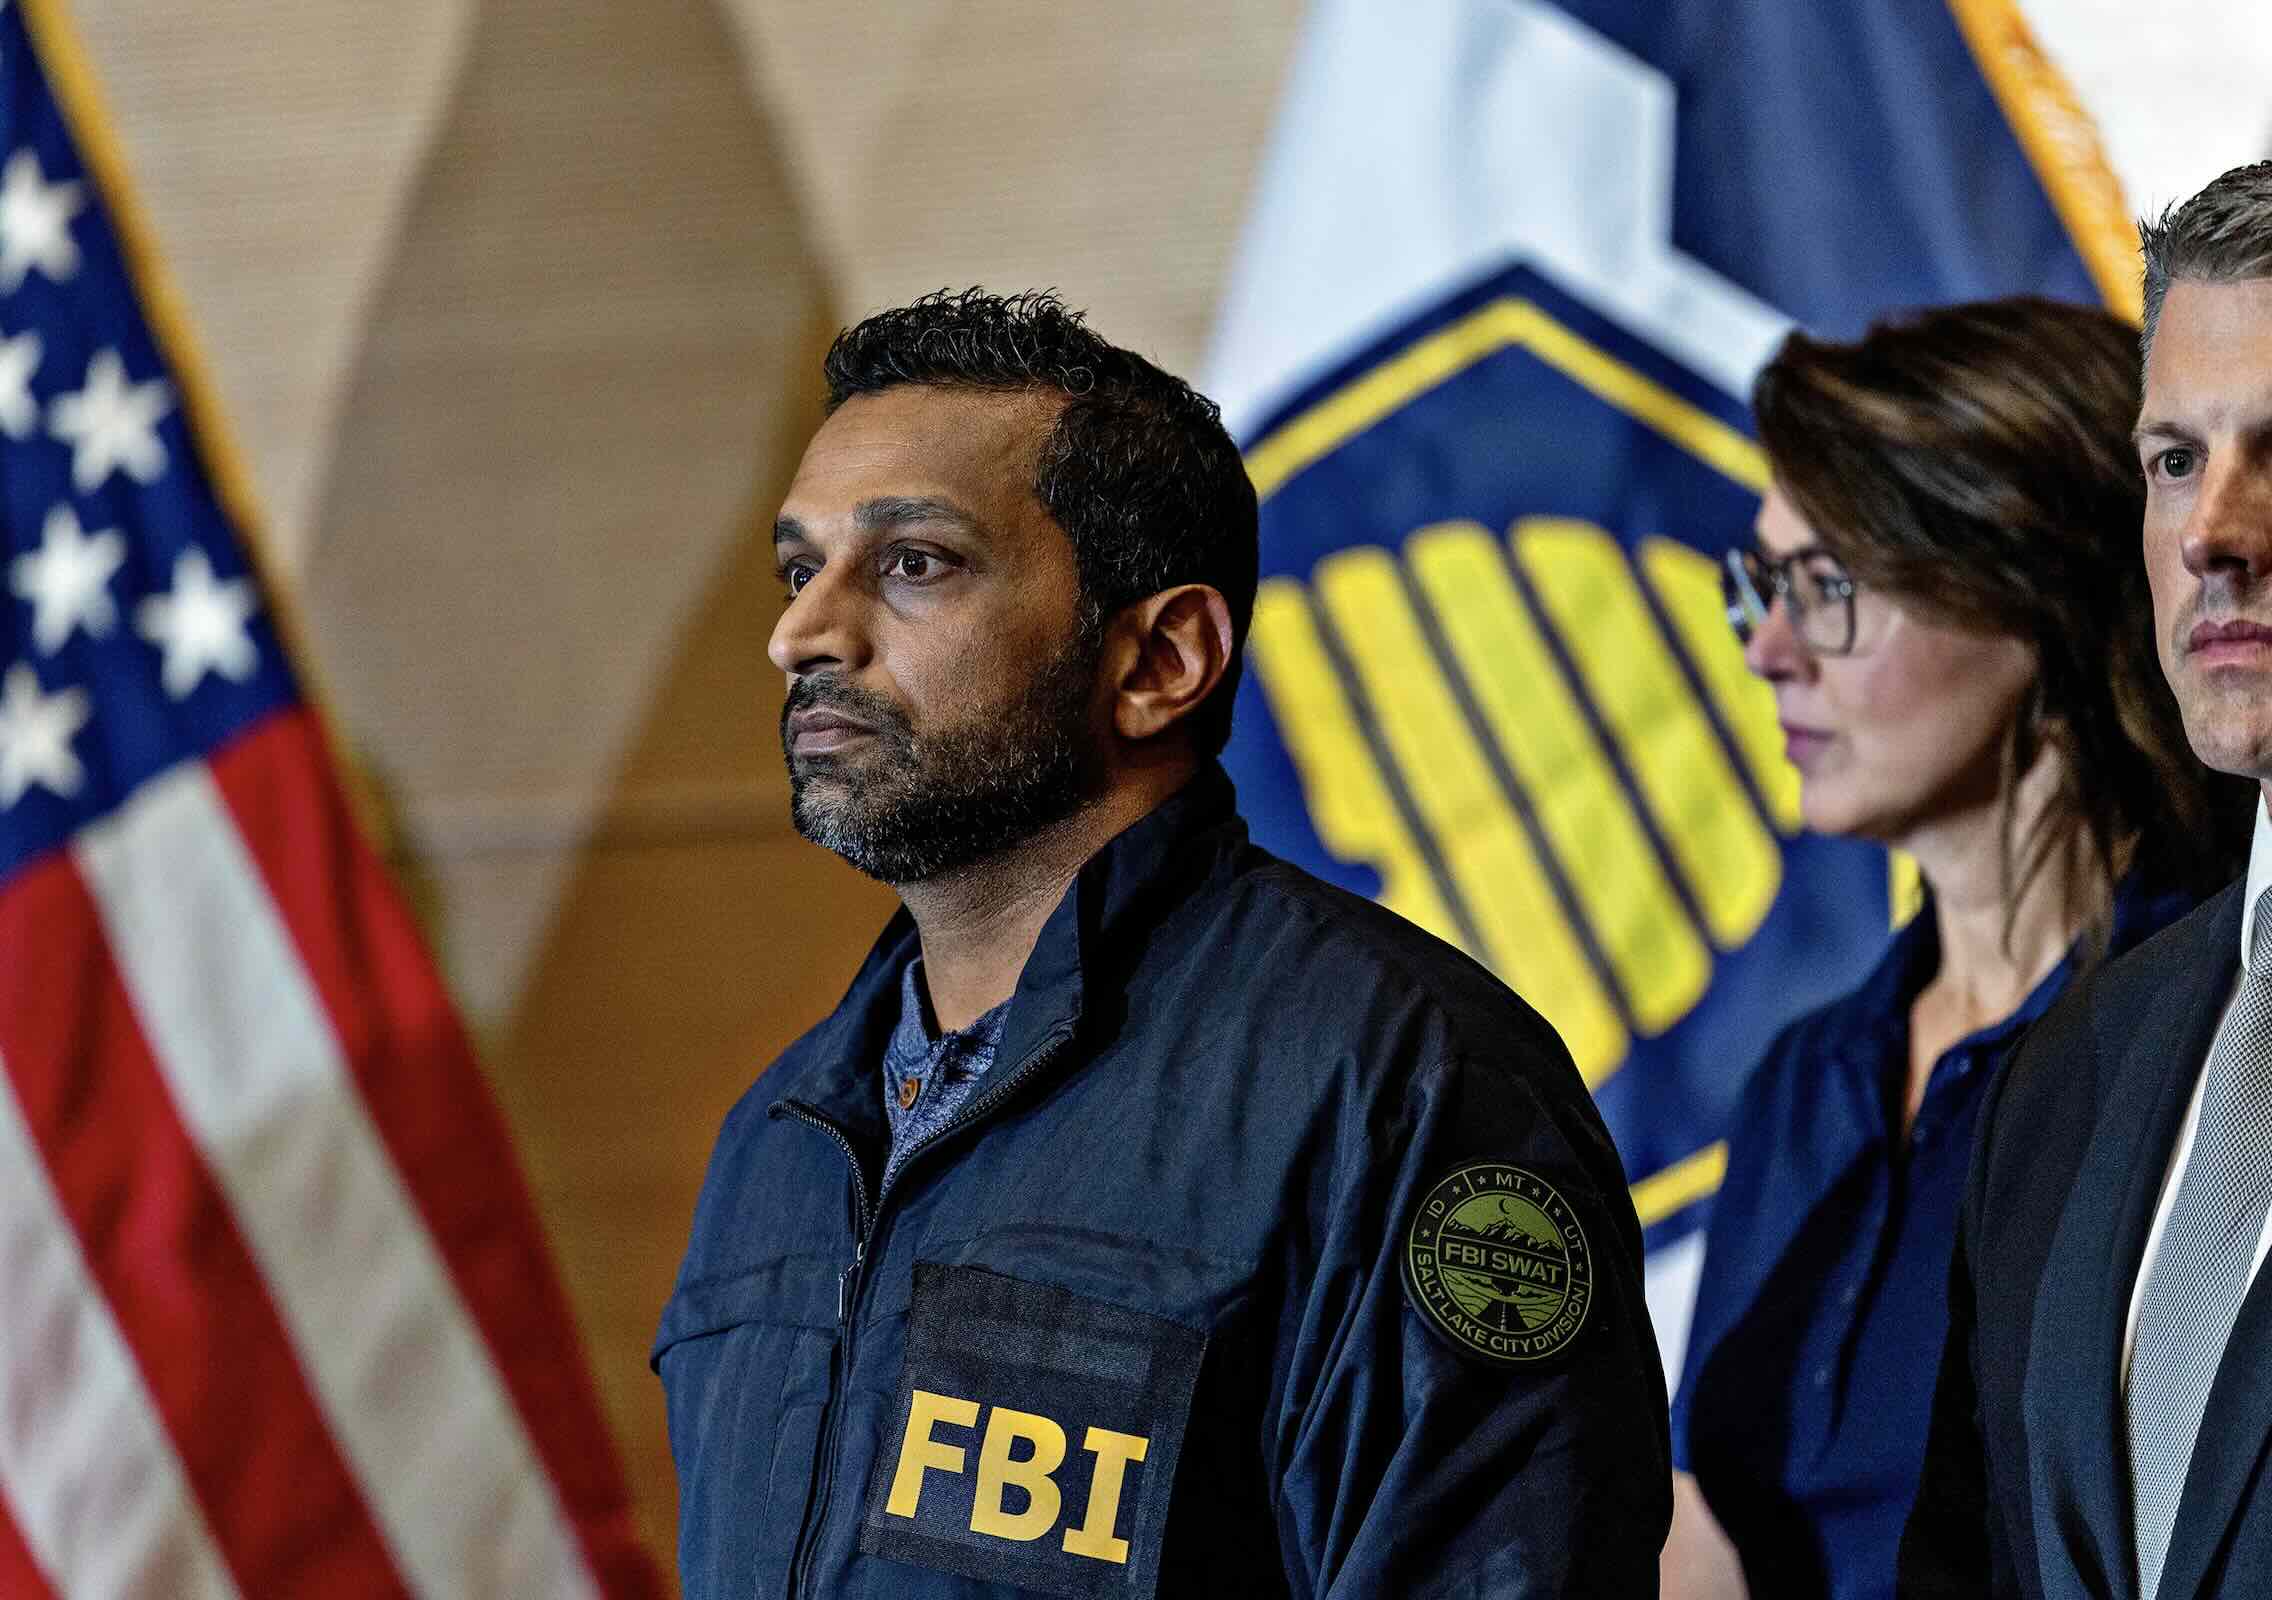
FBI Director Kash Patel | Photo: New York Times
When the extortion group ShinyHunters announced they had breached the FBI, the initial shock was met with a wave of disbelief. The Federal Bureau of Investigation, the premier law enforcement agency in the United States, compromised? The claim seemed almost absurd. However, as details emerged, the absurdity was replaced by a damning realization: the breach was not the result of a sophisticated, unstoppable cyber weapon. It was the result of a missed deadline and a three-month delay in applying a critical software patch.
The story begins not with the FBI, but with Oracle. In June 2026, Oracle released an emergency security update for its PeopleSoft PeopleTools software, a platform used by thousands of organizations, including the FBI, to manage human resources and recruitment. The flaw, tracked as CVE-2026-35273, was a critical vulnerability that allowed unauthenticated remote code execution. In simple terms, it allowed hackers to bypass the login screen entirely and run commands on the server as if they were the system administrator.
The flaw was severe enough that Oracle urged immediate action. For the FBI, which ran its public-facing recruitment portal, FBIjobs.gov, on this very software, the warning was a direct call to action. Yet, the patch was not applied. While the bureau likely has rigorous internal review processes for software updates, three months passed between the release of the fix in June and the breach in September.
How the Hack Worked
ShinyHunters did not start by targeting the FBI. They started by targeting the software. Between May and June 2026, they conducted a massive, automated scan of the internet using tools like Shodan and Censys, compiling a list of every IP address running a vulnerable version of PeopleSoft. FBIjobs.gov was on that list. When they decided to retaliate against the FBI for a public warning the bureau had issued about them, they simply checked their notes and tested the old exploit.
The attack itself was a multi-step "gadget chain" that exploited the unpatched flaw. This is how it worked.
- Step 1 — The Scan: Using internet-wide scanning tools, ShinyHunters identified FBIjobs.gov as running a vulnerable version of Oracle PeopleSoft.
- Step 2 — The Missing Authentication: The flaw (CVE-2026-35273) was in an internal administrative endpoint that completely lacked an authentication check. The software assumed any request reaching it had already been verified.
- Step 3 — The SSRF Trick: The hackers sent a specially crafted HTTPS request to the public-facing gateway. This triggered a Server-Side Request Forgery (SSRF) condition, tricking the gateway into forwarding the malicious request deeper into the internal network—straight to the unprotected admin servlet.
- Step 4 — Java Deserialization: The forwarded request contained a hidden malicious payload written in Java XML. The server's Java Virtual Machine interpreted the payload as an active command and executed it automatically, granting the attackers full command-line access. No username or password was ever required.
- Step 5 — The Pivot to AWS GovCloud: Once inside the recruitment infrastructure, the hackers found stored access keys and roles that allowed the job server to communicate with the FBI's backend HR database on AWS GovCloud. Because the public job site and the internal HR database were not properly segmented, the hackers rode those legitimate permissions across the digital bridge into the sensitive personnel data.
The initial break-in took milliseconds. The exfiltration of 2 to 3 terabytes of data—including names, Social Security numbers, home addresses, and personal contact details of active FBI agents and applicants—took hours or days. The stolen data also included the names and addresses of agents' spouses and family members, and medical screening logs from an internal portal called "MedLink."
The Preventable Failure
The technical post-mortem reveals a painful truth. The FBI's internal operational databases are strictly isolated, often air-gapped and impossible to reach from the public internet. However, their human resources cloud, hosted on AWS GovCloud, was not adequately segmented from the public-facing job site. The job portal, which had to communicate with the HR database to process applications, became a digital bridge for the attackers.
This was a failure of "cyber hygiene." A patch was available for over three months. The FBI had the resources and the expertise to apply it. The breach was not a failure of technology; it was a failure of process. The hack took milliseconds to execute once the malicious packet was sent, but it took months to become possible due to inaction.
What the Hackers Actually Want
Surprisingly, ShinyHunters is not demanding a multi-million dollar ransom. They have explicitly stated that this attack was not financially motivated. Instead, they want a formal retraction of an FBI statement about them.
In May 2026, the FBI issued a public safety advisory following a massive ShinyHunters attack on a school software system. In that alert, the FBI warned that the group uses extreme harassment tactics—such as sending threatening text messages, making terrifying phone calls to victims' families, and "swatting" targets (falsely reporting emergencies to trick armed police units into raiding a victim's home).
ShinyHunters strongly denies doing any of those things. They claim that other "low-skilled" hackers have merely been abusing their name to carry out those operations. The hackers gave FBI Director Kash Patel and the assistant director of the cyber division a one-week deadline to "correct or simply REMOVE" the warning advisory. They framed the entire FBI breach as proof that their capabilities are real and shouldn't be lied about, writing: "This PSA today is living evidence of that."
When media outlets asked if this was a standard extortion attempt, a group representative told 404 Media, "what we plan to do is not something I'd call extortion, maybe coercion."
If the FBI refuses to retract the report, the hackers have dropped hints that they will publish the remaining terabytes of agent profiles online. If that happens, cybersecurity analysts fear the group will sell the data to foreign intelligence agencies or hostile nation-states who are highly eager to get their hands on active FBI rosters.
The FBI is now investigating the breach, but the damage is done. The lesson is stark and universal: in cybersecurity, speed matters. A patch is only effective if it is actually installed. For the FBI, a three-month delay in a routine update was all it took to turn a public jobs portal into a national security liability.
No Ads. By Us. For Us.
This article was made possible by readers like you. We hope it inspired you to support Emerald Book, so we can continue producing content like this.
We will never show you ads, sell your data, or require a subscription to consume our content. Your gift helps us keep the truth accessible.
Click the Support button to give a gift of any amount today.
Thank you for making this work possible.